
AgentOps for Kubernetes fleets, done safely.
An MCP server that lets AI agents operate a multi-cluster Kubernetes fleet through an Open Cluster Management hub. The agent never holds a kubeconfig. Every write is policy-checked, human-approved, and traced.
📖 Docs site · ⭐ Repository · 📦 PyPI · 🚀 Releases
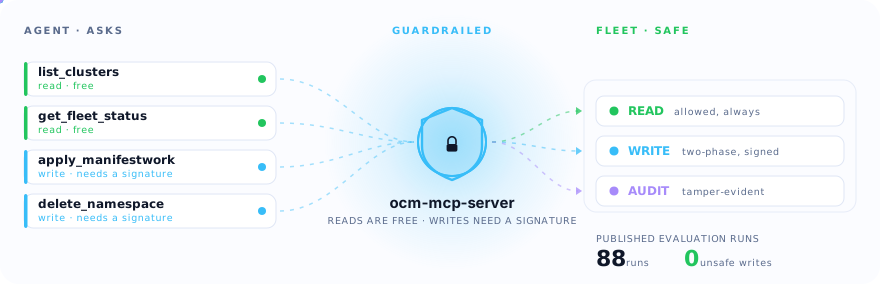
- Reads are free. Inventory, health, placement, add-ons and events across every managed cluster, answered straight away.
- Writes go through a gate. A change is proposed, a person signs that exact content with an Ed25519 key on their own terminal, and only then is it applied, once.
- Four independent layers can each refuse a write: the server's own guardrails, Kyverno on the hub, the human approval, and Kubernetes RBAC.
- Dangerous capabilities don't exist. No tool reads Secrets, execs into a pod, or deletes what it did not create, so none can be prompt-injected into use.
- Everything is audited in a tamper-evident log, with OpenTelemetry tracing.
pip install ocm-mcp-server      # or: uvx ocm-mcp-server
ocm-mcp doctor                  # checks every read tool against your hub, writes nothing
Then point any MCP client (Claude Code, Codex, Gemini, VS Code, IBM Bob) at the ocm-mcp-server command.
The Getting Started guide walks through a local three-cluster fleet in about fifteen minutes.
| ocm-mcp-server | The server, its guardrails, Kyverno policy pack, Helm chart, evaluation harness and docs |
| ocm-mcp-server.github.io | The published docs site, built from the main repository's own markdown |
Issues and pull requests are welcome. Read the contributing guide first. Report security issues privately through a security advisory, never in a public issue.
Apache-2.0 · Maintained by @sandeepbazar
